security-guidance for Claude Code: review, how it works and whether it is worth it (2026)
Before you start
- 9 min read
Boxes marked Run in terminal are what you type; plain text explains why.
What you get in one minute#
security-guidance is a free Anthropic plugin that checks the code Claude writes for security mistakes, in three layers, and it is worth having for web or server code if you can spare the extra model usage.
Logo: the official Claude Code logo from Anthropic's press kit (anthropic.com/press-kit)
The marketplace page shows 241,800 installs (October 2026). It never blocks anything: it hands findings back to Claude.
| Verdict | Detail |
|---|---|
| Useful? | Mostly. The free regex layer is a safe add. The two Opus review layers add real checking but cost usage and have had many bugs. |
| Best for | Web, API and server code written mostly by Claude, in git repositories. |
| Skip it if | You have tight usage limits, no git, or code that must not leave your machine. |
| Made by | Anthropic, Apache 2.0 licence. |
| Version + date | 2.0.17, 27 October 2026 (same in the marketplace entry). |
| Install command | /plugin install security-guidance@claude-plugins-official |
| Token cost | No published figure. It adds no skills or agents; the cost is the model reviews. The README shows one sample Stop review: 31,994 tokens in, 3,250 out, about $0.19 at list price. |
What it does#
You do nothing: once installed, it runs by itself while Claude works. There is no command to type.
- Layer 1, each edit: 25 text rules (for example
eval(,innerHTML,pickle,yaml.load, GitHub Actions files) warn Claude at once. No model, no cost. - Layer 2, each finished turn: the changes of that turn go to an Opus review in the background. Findings come back to Claude to fix.
- Layer 3, each
git commitorgit pushClaude runs: an agent reads related files to trace data flow, for bugs a single file hides. - Your own rules: add
claude-security-guidance.md(text for the reviewer) orsecurity-patterns.yaml(extra regex rules). - Added to Claude Code: 5 hook events, 0 skills, 0 slash commands, 0 agents, 0 MCP servers. The marketplace page still describes an older "pre-tool hook".
How it works in the background#
Python hooks watch three moments, and each layer feeds its findings back into Claude's context. The picture follows one change.

- Background reviews use
asyncRewake: a hook that exits with code 2 wakes Claude with the findings (hooks docs). - Caps: 30 files per turn, 3 fix rounds in a row, 20 commit reviews per hour.
Under the hood: dissection#
security-guidance is about 12,000 lines of Python and Bash hooks, with no skills or prompts to load: it is real code that runs on every prompt, edit, stop and commit.
The file tree#
security-guidance/
├── .claude-plugin/plugin.json     name, version 2.0.17
├── LICENSE                        Apache 2.0
├── README.md                      settings, privacy, cost
├── hooks/
│   ├── hooks.json                 5 hook events, all run through sg-python.sh
│   ├── sg-python.sh               Bash: finds a working Python 3
│   ├── ensure_agent_sdk.py        builds the venv, installs claude-agent-sdk
│   ├── security_reminder_hook.py  the main hook: every event ends here
│   ├── patterns.py                the 25 regex rules and their warnings
│   ├── llm.py                     the model calls and the reviewer prompts
│   ├── review_api.py              API request helper
│   ├── gitutil.py, diffstate.py   git snapshot, diff, caps, state
│   ├── reporesolve.py             finds the repo to review
│   ├── extensibility.py           loads your rule files
│   ├── session_state.py, _base.py state, logging, output format
└── tests/                         45 test files
What each file is#
| File | Language | What it does | When it runs |
|---|---|---|---|
hooks/hooks.json | JSON | Registers the hooks and their filters | Always |
hooks/sg-python.sh | Bash | Probes python3, python, py -3; runs the script | Before every hook |
hooks/ensure_agent_sdk.py | Python | Creates ~/.claude/security/agent-sdk-venv, runs pip install claude-agent-sdk | Session start |
hooks/security_reminder_hook.py | Python | Snapshot, pattern check, Stop and commit reviews | Prompt, edit, stop, commit |
hooks/patterns.py, llm.py | Python | Rules; prompts and model calls | Edit; Stop and commit |
hooks/gitutil.py, diffstate.py | Python | Git snapshot and diff, state, de-duplication | Prompt and Stop |
Key excerpts#
hooks/hooks.json, the commit review:
{ "type": "command",
  "command": "bash \"${CLAUDE_PLUGIN_ROOT}/hooks/sg-python.sh\" \"${CLAUDE_PLUGIN_ROOT}/hooks/security_reminder_hook.py\"",
  "if": "Bash(git*commit*)", "asyncRewake": true }
hooks/patterns.py, one of 25 rules:
"ruleName": "eval_injection",
"regex": r"(?<![a-zA-Z0-9_\.])eval\(",   # skips model.eval(), redis.eval()
Disk and network#
- Writes:
~/.claude/security/(state, a log that rotates at 1 MB, the venv), temporary git index copies, and your optional rule files are read. - Network:
pip install claude-agent-sdkonce (unpinned), then model calls. By default your diff hunks, paths and file contents go toapi.anthropic.com, or to your gateway or cloud provider. - Needs: Bash, Python 3.10+ for the agent review, git, and a Claude sign-in or API key.
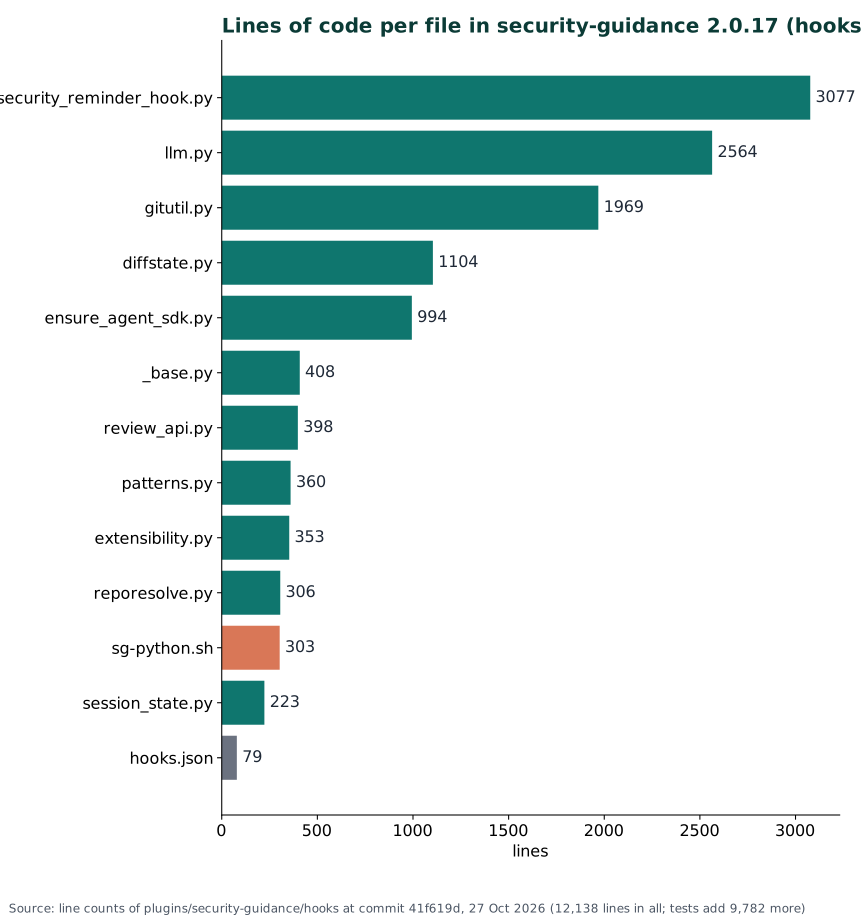
Chart: line counts from the plugin folder at commit 41f619d, 27 October 2026.
What users say#
27 reports read: 2 praise, 4 mixed, 21 complaints, but that split is skewed. GitHub issues attract complaints. Most name versions 2.0.6 to 2.0.13, not 2.0.17, and we did not test the fixes. Hacker News had no thread; Reddit was not read.
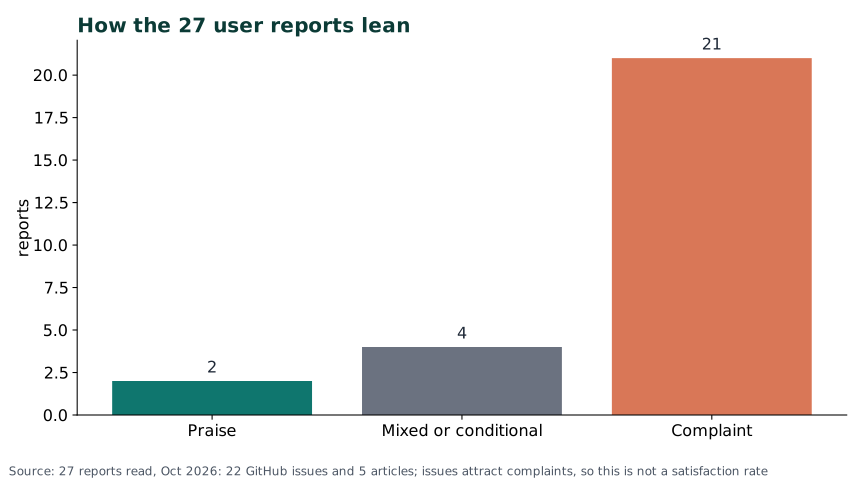
Chart: our count of the 27 reports, October 2026. Not a satisfaction rate.
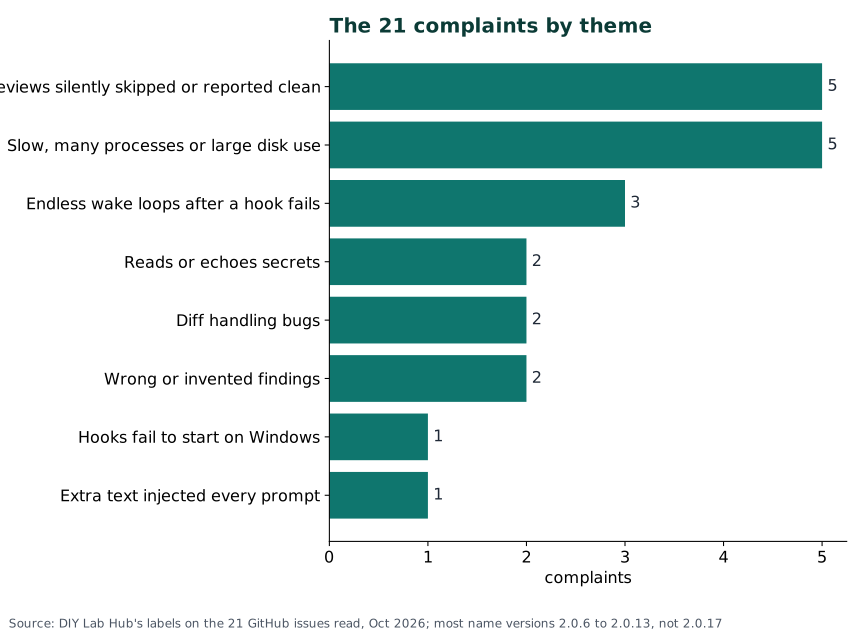
Chart: themes of the 21 complaints, labelled by DIY Lab Hub, October 2026.
| Voice | What they say |
|---|---|
| Praise | Inventive HQ (June 2026) calls it a useful shift-left control, still no replacement for scanners. |
| Mixed | Help Net Security (May 2026) repeats Anthropic's own "30-40% fewer security comments" with no independent data. |
| Silent skips | An issue (October 2026): subscription logins never ran the model reviews. |
| Cost | An issue (August 2026): about 200k tokens over 77 commit reviews, zero findings. |
| Loops | An issue (September 2026): a failing Stop hook re-woke the model about 30 times. |
| Secrets | An issue (August 2026): the review echoed OAuth tokens into the transcript. |
Pros: why it is useful#
It adds a second pair of eyes on Claude's code at almost no effort, and it is built by Anthropic.
- Free first layer: the regex rules cost nothing and add context only when a rule matches.
- Separate reviewer: layers 2 and 3 start from the diff in a fresh context (docs), so Claude does not grade itself.
- Cross-file bugs: the commit reviewer reads callers and sanitizers, which one-file checks cannot.
- Tunable: a cheaper model, any layer off, and your own rules.
Cons: why it is not useful#
It costs usage, sends code to a model, and has been buggy.
- Cost: Opus reviews each turn and commit; no in-session cost view.
- Privacy: diffs and file contents leave your machine.
- Quality: false positives and a few invented findings were reported.
- Gaps: commits you run yourself are not reviewed; no dependency or CI scanning.
- Overlap with
/security-reviewand the Claude Security plugin.
Should you consider it? When it is useful#
Consider it for web, API and server code, and tune it first; skip it for throwaway scripts or if code cannot leave your machine.

| Situation | Verdict |
|---|---|
| Claude writes web or API code that ships | Install |
| Tight usage limits | Install with SECURITY_REVIEW_MODEL=claude-sonnet-5-5 |
| Private code, no model sharing | Regex layer only: ENABLE_CODE_SECURITY_REVIEW=0 |
| Throwaway scripts, no git | Skip it |
Install and check it#
One command inside Claude Code installs it from Anthropic's official marketplace. You need Python 3.10+ and git.
Linux#
/plugin install security-guidance@claude-plugins-official
Or from your shell: claude plugin install security-guidance@claude-plugins-official.
Windows (PowerShell)#
Install Git for Windows first (the hooks run through Bash), then:
claude plugin install security-guidance@claude-plugins-official
Mac (Terminal)#
claude plugin install security-guidance@claude-plugins-official
Check it worked#
claude plugin list
Then ask Claude to write a file containing eval(userInput): a "Security Warning: eval() executes arbitrary code" note should appear. The log is ~/.claude/security/log.txt ($HOME\.claude\security\log.txt on Windows). If /plugin is "not available in this environment", use the shell command above.
Things to keep in mind#
- Security: it runs your Python on every prompt and edit, and installs the latest
claude-agent-sdkfrom PyPI at session start. Readhooks/hooks.jsonfirst. - Privacy: your
claude-security-guidance.mdis added to every review prompt: no secrets in it. - Update channel: the marketplace; versions move fast (2.0.6 to 2.0.17 in about four months of the issue reports).
- Conflicts: none known; it overlaps with
/security-review. - Organisations can switch it on with
enabledPlugins, or block marketplaces. - Off switches:
SECURITY_GUIDANCE_DISABLE=1, or/plugin disable security-guidance@claude-plugins-official.
Troubleshooting#
| Problem | Solution |
|---|---|
SessionStart:startup hook error ... execvpe(/bin/bash) failed (Windows) | bash resolves to the WSL stub (issue 2697); install Git for Windows and put its bash first. |
Log says LLM review disabled or no API credentials | Sign in with /login or set ANTHROPIC_API_KEY. DISABLE_TELEMETRY and DO_NOT_TRACK stop the sign-in reaching the plugin. |
Commit security review did not complete: ... | Read ~/.claude/security/log.txt; check git, Python 3.10+ and the network. |
| "Background security review" keeps repeating | The hook cannot start (often a bad Python). Disable the plugin, update, restart. |
| Every prompt is slow on WSL | Keep the repo off /mnt/c, or set ENABLE_STOP_REVIEW=0 (issue 6854). |
Marketplace "claude-plugins-official" not found | /plugin marketplace add anthropics/claude-plugins-official, then install again. |
FAQ#
Is it made by Anthropic? Yes. It is in Anthropic's own marketplace, listed as "Anthropic verified".
Does it block bad code? No. Findings go to Claude as instructions; nothing stops a write or a commit.
How do I make it cheaper? Set SECURITY_REVIEW_MODEL and SG_AGENTIC_MODEL to a smaller model, or turn the model layers off.
Does it replace /security-review or CI scanning? No. The docs call it one layer next to /security-review, Code Review and your own scanners.
Sources#
- security-guidance in anthropics/claude-plugins-official: README,
hooks/,plugin.jsonand the marketplace entry at commit 41f619d (27 October 2026). - Catch security issues as Claude writes code, Hooks reference and the marketplace listing: official pages (October 2026).
- User reports, GitHub issues in claude-plugins-official: 5067, 6609, 6355, 5331, 5330, 5558, 6854, 5934, 5066, 6097, 2697, 2011; in claude-code: 96860, 99840, 98731, 92146, 96148, 96276, 90010, 102567, 101548, 85421 (May to October 2026).
- Articles: Help Net Security (May 2026), mer.vin (May 2026), Inventive HQ (June 2026), VibeDoctor (September 2026), apito.ai (2026).
Not run by DIY Lab Hub: we read the code and docs but did not install the plugin on a test machine.
Checked against the official docs on 2026-10-27